
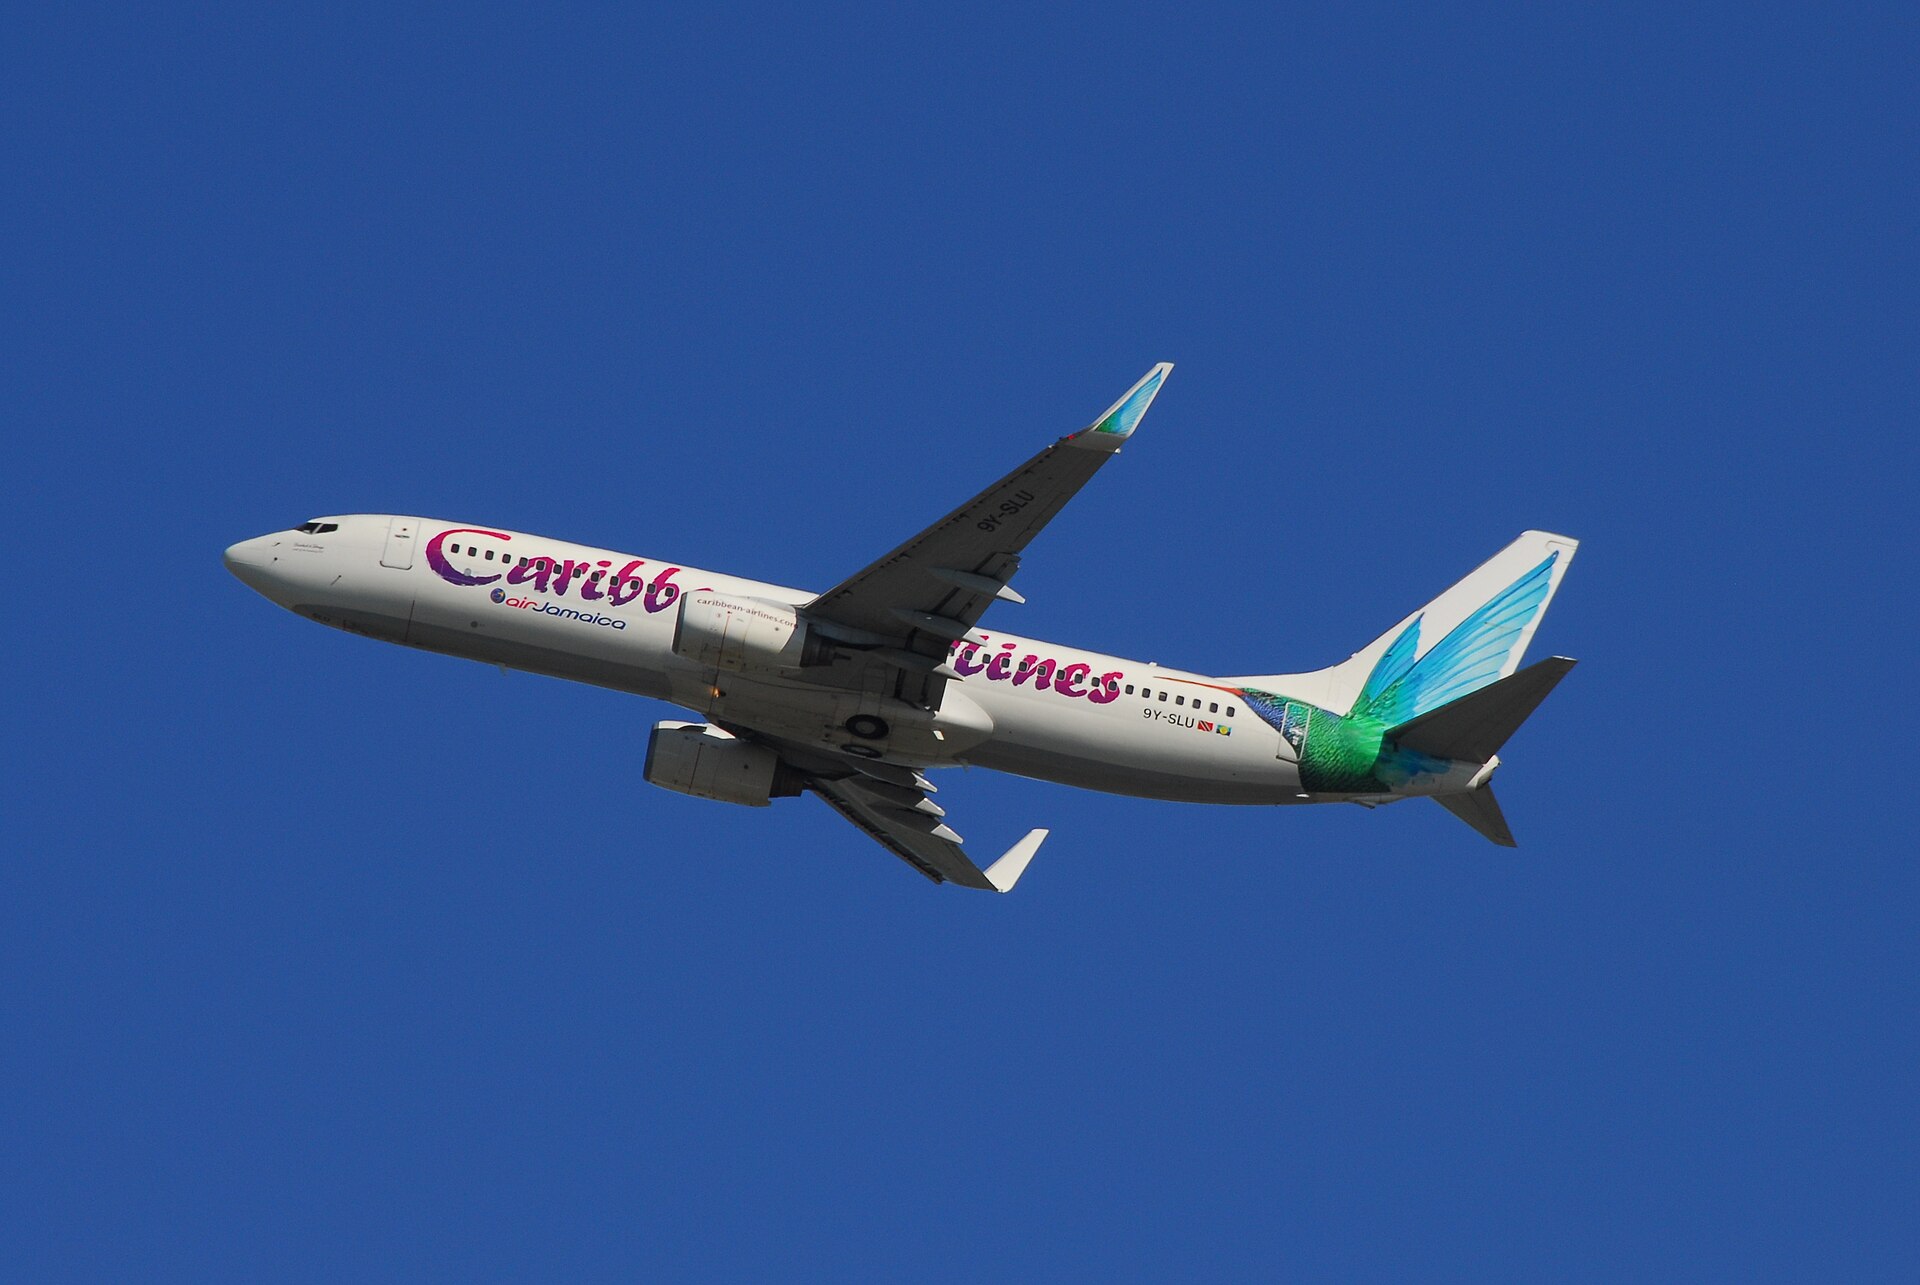
Caribbean Airlines, the flag carrier of Trinidad and Tobago, said by Sunday 15 November 2026 that an unauthorised party reached booking and reservation data held by a travel technology supplier. The airline says the breach was limited to booking and travel related data.
The system belongs to Amadeus, a Spanish travel technology company that runs reservation software for airlines worldwide. Other carriers had already reported impact from the same incident in late October and early November 2026.
Cathay Pacific and Singapore Airlines, two other customers of the same supplier, each reported tens of thousands of affected records. Caribbean Airlines has not said how many customers it counts among them.
Key Facts
- Who Caribbean Airlines, flag carrier of Trinidad and Tobago, and Amadeus, its travel technology supplier.
- What An unauthorised party reached booking and reservation data; preliminary findings point to no payment card data.
- Where Amadeus reservation systems, used by many airlines worldwide.
- When The airline confirmed it by Sunday 15 November 2026; customer notification is under way.
- As of 16 November 2026, 07:30 GMT
Caribbean Airlines is the latest carrier touched by one supplier incident. It says the breach was limited to booking and travel data.
What We Know
In its statement, public by 15 November 2026, Caribbean Airlines said Amadeus told it that an unauthorised party exploited a vulnerability to access booking and reservation information. The airline said it is notifying affected customers and the process is under way.
The airline also said preliminary findings from Amadeus suggest no payment card data was accessed. It apologised for the concern and inconvenience.
The airline has not listed which fields were accessed for its own customers. A booking reference, the code that identifies a reservation, is among those Cathay Pacific listed.
The airline has not said how many customers are affected. It describes the breach as limited to booking and travel related data.
In its statement of October 2026, Amadeus said it became aware of a vulnerability affecting a travel booking display environment, where certain booking-display data was accessible. It said it implemented measures to fix the vulnerability and enhanced monitoring and detection.
Amadeus said it has no evidence that payment or financial data was accessed. It added that its investigations are ongoing and that it sees no indication of a ransomware purpose, meaning an attack meant to lock data for a ransom.
Why It Matters for Travellers
Cathay Pacific, the Hong Kong airline, said in its notice of 30 October 2026 that Amadeus told it of unauthorised access on Wednesday 28 October 2026. About 53,000 of its bookings were affected, and access ran between August 2023 and September 2026 using login credentials assigned to an Amadeus system account.
In most of those cases the information accessed included a booking reference, passenger name and flight details, Cathay said in the same notice. A smaller subset may also have held email and phone contacts, a travel document number or a frequent flyer number.
Booking references and names can be used to pose as an airline, a common phishing tactic. Phishing means fraudulent messages built to steal money or personal data, and a message that cites a real trip looks more genuine.
Airline booking data often sits with a supplier rather than with the carrier itself, which is why one incident can reach many airlines at once. Our earlier piece on the airline cutting routes in the eastern Caribbean shows how widely it serves the region.
Singapore Airlines, the flag carrier of Singapore, put its own figure at about 46,000 records in early November 2026. The share of the breach that touches Caribbean Airlines is not stated.
Malaysia Airlines, the flag carrier of Malaysia, and Thailand’s Thai Airways also reported impact from the same incident. Amadeus has not published a total for all airlines.
What Is Not Known
Caribbean Airlines has not said how many customers are affected. It has not said when Amadeus told it of the incident.
Amadeus describes its investigations as ongoing, so its findings are not final. Until they close, the point that no payment data was touched rests on preliminary work.
What to Watch
No date is confirmed for the next steps. Amadeus said its investigations continue, and Caribbean Airlines said notification of affected customers is under way.
Readers who follow regional security stories can compare this case with the data breach at a Jamaican payments firm in October. More coverage sits in our Caribbean hub.
Frequently Asked Questions
What did Caribbean Airlines say happened?
It said Amadeus informed it that an unauthorised party exploited a vulnerability to access booking and reservation information. The airline said the breach was limited to booking and travel related data.
Was payment card data taken?
Caribbean Airlines said preliminary findings from Amadeus suggest no payment card data was accessed. Amadeus said in October 2026 it had no evidence that payment or financial data was accessed.
What data may be affected?
Caribbean Airlines has not listed the fields. Cathay Pacific, another Amadeus customer, said most affected records held a booking reference, passenger name and flight details.
Will the airline contact affected passengers?
The airline says it is notifying affected customers and the process is under way. It has not said how many customers are affected.
Sources: Amadeus statement, October 2026; Cathay Pacific notice, 30 October 2026; Caribbean Airlines statement, public by 15 November 2026.
This article was produced by The Rio Times’ automated AI newsroom. Editorial responsibility: Matthias Camenzind, Publisher and Editor-in-Chief. The Rio Times also runs Ask Rio Times, which answers from 100,000+ of our own articles, the daily Latin America Power Map, and prediction-market odds on elections and markets.. How we use AI · Report an error